About
We started because backlogs were growing, not shrinking.
Founded in 2023. Based in Tel Aviv. Built by application security researchers who saw the same pattern at every org: more findings, same slow remediation, no fix in the ticket.
2023
Founded in Tel Aviv
2
Co-founders with AppSec and tooling backgrounds
IL
Independently funded startup
Team
The people building Tenzai
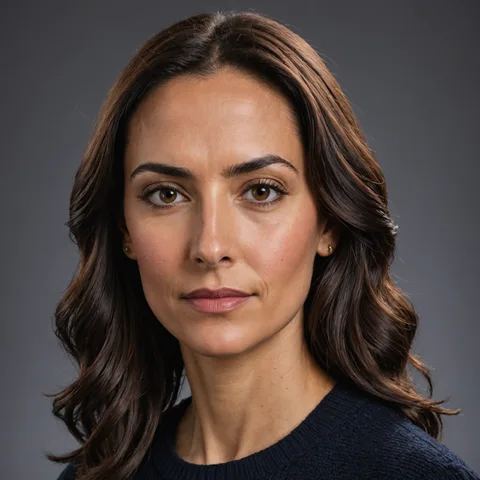
Yael Kochman
Co-founder and CEO
Has led application security programs and run AppSec practices for B2B software teams. The recurring problem was always the same: scanner findings piled up faster than any team could close them without a path to the actual fix. Co-founded Tenzai to close that gap.
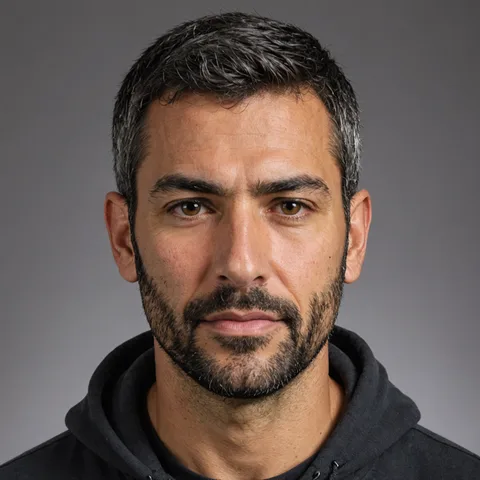
Ariel Ben-David
Co-founder and CTO
Background in static analysis tooling, compiler internals, and distributed systems, with years building vulnerability detection engines for code analysis platforms. Designed Tenzai's hybrid SAST and call-graph analysis engine to surface real issues without the false-positive noise that causes scanner fatigue.
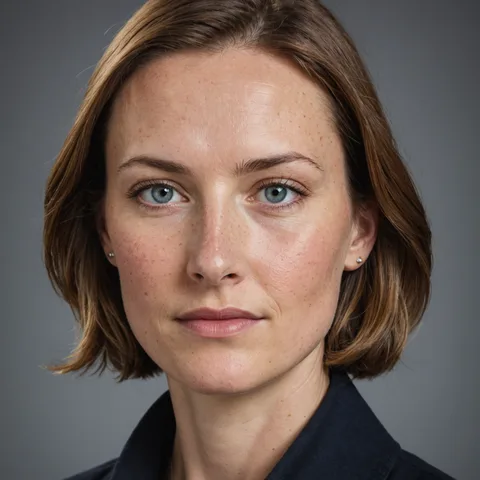
Sophie Laurent
Head of Security Research
CVE researcher and pen testing practitioner who turned to tool-building after years analyzing exploit chains. Leads Tenzai's detection rule library and oversees fix proposal accuracy against the OWASP and CWE taxonomy.
Mission
Every finding should come with a path to fixing it.
Security scanners are good at finding problems. They are not designed to help developers close them. That gap, the distance between a finding and a reviewed fix, is where security backlogs live.
We built Tenzai around the premise that a finding without a proposed fix is an incomplete result. Our platform combines automated scanning with AI-generated, scoped fix proposals so that every finding a developer receives includes the next step: a specific code change to review and apply.
That does not mean AI fixes every issue automatically. The developer reviews, decides, and applies. Tenzai prepares the work so a developer can make that decision in minutes instead of hours.
We are a small, independently funded team based in Tel Aviv. We work directly with security leads and engineering teams at startups and growth-stage companies who are serious about reducing their vulnerability exposure without adding headcount.
Start closing findings, not just cataloging them.
Free plan available. No credit card required.